Pass your security audit.
Close your enterprise deal.

An enterprise prospect or your investors are waiting on your SOC 2 report, and your cloud controls are not there yet, with or without a compliance platform telling you so. Start with a free gap assessment, then get to Type I for $5,000 fixed, backed by a money-back guarantee. Zero failed audits to date.

Book a 15-minute call
  • Free gap assessment first
  • SOC 2 Type I: $5,000 fixed
  • Delivered on AWS, Azure and GCP

No pitch. Your gap assessment is free, and no billable work starts until you approve the plan.

Questions first? Talk to Riley, our AI front desk: live in your browser, or by phone at +1 267 460 7396.
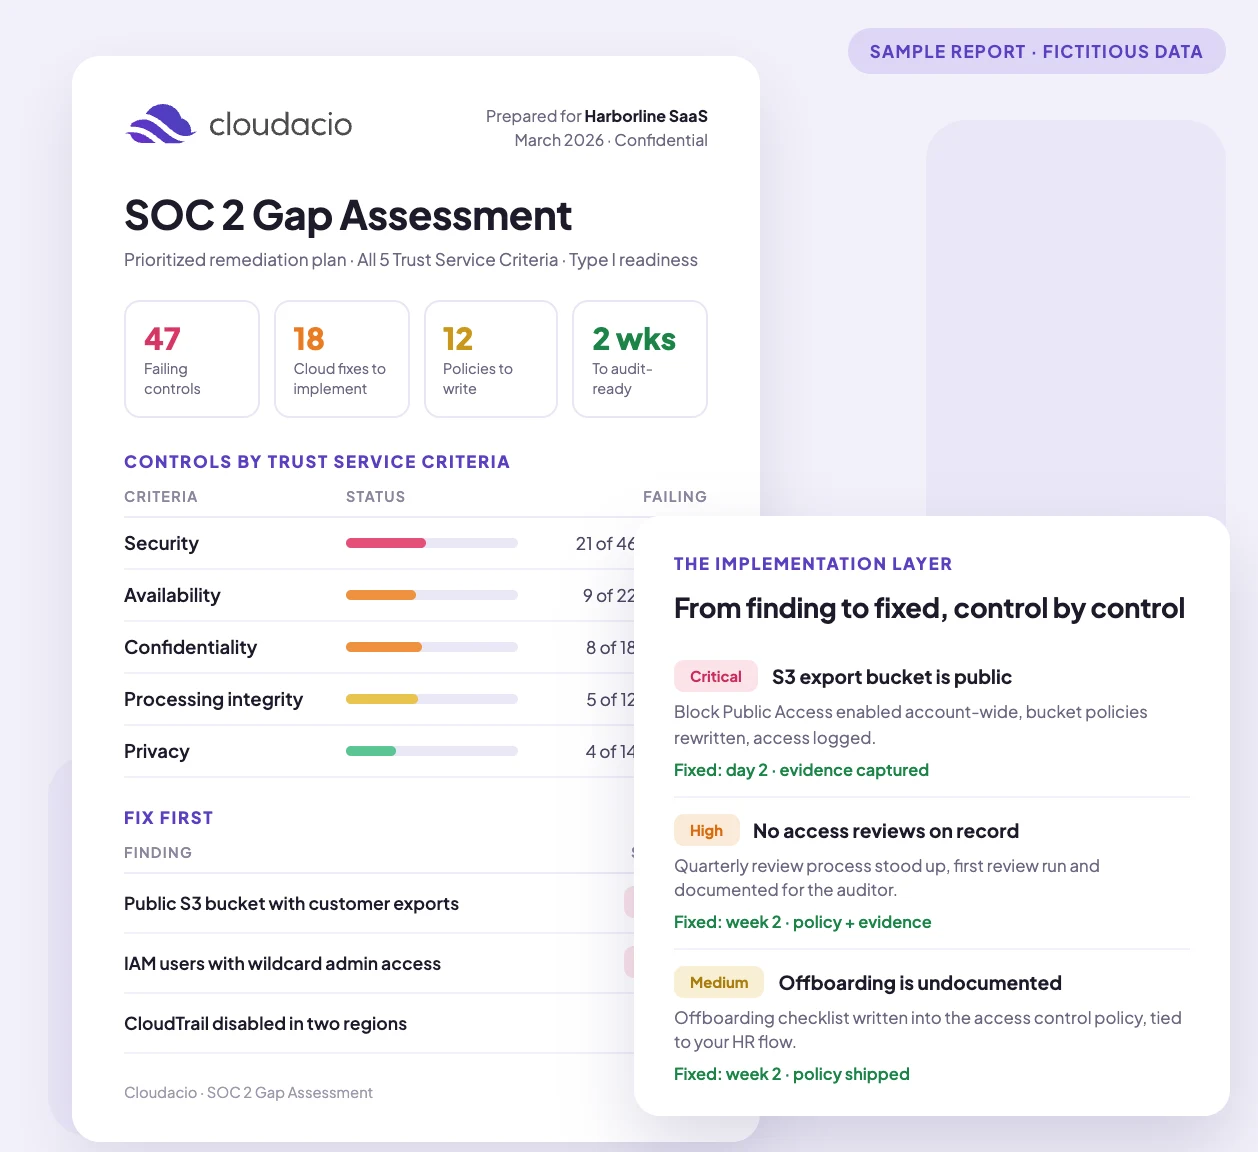
Sample SOC 2 gap assessment report: control status by Trust Service Criteria and a prioritized remediation plan

See how it works

Trusted by Leading Companies

Samsung Condé Nast EzLogz Language Testing International Mereos TrueClaim InfraNET Bankingly Exceleron ChurchSpring Occulytics Genalyte ServiceHub Advanced Training Academy ActBold BidFire DynaBliss MaetaData Consentz JoyVoo Rivelio COSA CitizenNet Cloud Computing Consultants CodeEnigma Phasic Energy VinoVoss UpViral Terra Universal Level Up Village Samsung Condé Nast EzLogz Language Testing International Mereos TrueClaim InfraNET Bankingly Exceleron ChurchSpring Occulytics Genalyte ServiceHub Advanced Training Academy ActBold BidFire DynaBliss MaetaData Consentz JoyVoo Rivelio COSA CitizenNet Cloud Computing Consultants CodeEnigma Phasic Energy VinoVoss UpViral Terra Universal Level Up Village

Our Partners

AWS Partner NetworkGoogle Cloud PartnerMicrosoft Partner
DrataVanta

SaaS companies trust Cloudacio to turn failing controls into a clean SOC 2 report.

We've taken companies from failing controls to a clean report, again and again. Here's what an engagement delivers:

2 Weeks

From access granted
to Type I audit-ready

All 5

Trust Service Criteria
mapped in your free gap assessment

Zero

Failed audits where we
managed readiness
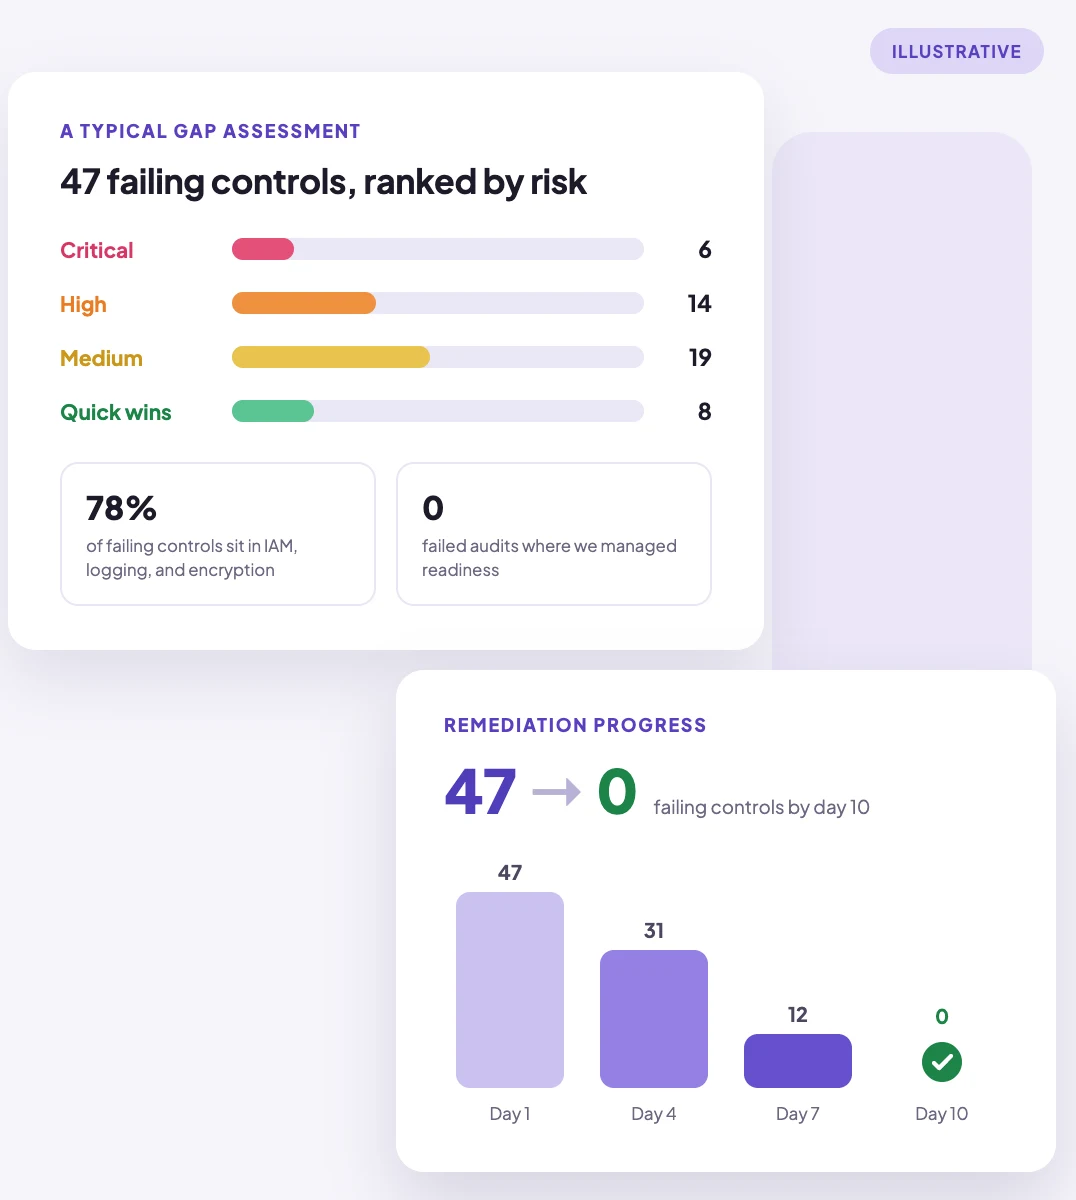
Illustrative gap assessment summary: failing controls by Trust Service Criteria and remediation progress to audit-ready
THE PROBLEM

Your Compliance Tool Found the Problems. Now What?

Vanta, Drata, and Sprinto are great at tracking what's wrong. They don't fix it. Your dashboard flags every failing control, and someone still has to make them pass. That's us.

Platforms track. They don't fix.

Your compliance platform flags every failing control: S3 public, IAM over-permissioned, CloudTrail missing. But it doesn't implement the fixes. Someone still has to.

Most teams with a compliance platform spend 3–6 months stuck on implementation.

Consultancies charge enterprise prices

Coalfire and Latacora are excellent if you're enterprise. At Series A or B, a multi-month SOW at $250/hr to fix IAM and logging is overkill and out of reach.

We deliver the same cloud remediation at a fixed price a seed company can afford.

The deal is waiting. The clock isn't.

An enterprise prospect sent a security questionnaire, or an investor requires SOC 2 before close. Your engineers should be shipping product, not configuring CloudTrail at 11 PM.

We've run deal-driven engagements in as little as 45 days to a Type I report.
IS THIS FOR YOU?

SOC 2 Readiness Is Built For Teams Like Yours

Deal-Driven Urgency

An enterprise prospect just sent you a security questionnaire, or an investor requires SOC 2 before close. You need a team that can hit the deadline and close the deal on the other side.

First-Time SOC 2

You've never been through a SOC 2 audit and don't know where to start. You need someone who's done it dozens of times: from gap assessment to control design to auditor selection to the final report.

On Vanta, Drata, or Sprinto and Stuck

Your compliance platform is tracking 47 failing controls, but nobody is fixing them. We're the implementation layer your platform doesn't have. We make the failing controls pass.

THE SOLUTION

From Failing Controls to Audit-Ready in 4 Phases

We fix the cloud controls, write the policies, collect the evidence, and coordinate the audit. Your engineers keep shipping. You get the report.

Gap Assessment

We map your current environment, security controls, and policies against the SOC 2 Trust Service Criteria. You get a clear picture of where you stand and exactly what needs to change, before any work begins.

Full mapping against all 5 Trust Service Criteria
Prioritized remediation plan with owners and timelines
Current-state documentation of your security posture
Free: no billable work until you approve the plan

Policy Writing

15+ policies from our library, adapted to your company and your infrastructure, with one revision round. We design and document the controls and set up evidence collection in your compliance platform.

15+ policies from our library, adapted to your company
Control design scoped to your actual stack and team size
Evidence collection system built and organized for auditors
Runs on your compliance platform: Drata, Vanta or Sprinto

Implementation & Evidence

We work alongside your engineering team to implement missing controls: access reviews, logging, incident response, vendor management. We collect and organize all audit evidence in a format auditors actually want.

Access control and identity management controls implemented
Logging, monitoring, and encryption controls configured
Full evidence repository organized and mapped to controls
Vendor and subprocessor review program built and managed

Audit Coordination

We introduce you to auditors from our network, prep your team for interviews, and act as your liaison through the audit. When you get your report, you'll understand every finding and how to address it.

Introduction to auditors from our network
Team prep for auditor interviews and walkthroughs
We attend the kickoff and take the auditor's questions for 30 days after handoff
30 days of post-audit support: the auditor's questions answered, your fixes guided
Book a 15-minute call

See How SOC 2 Readiness Works.

What the gap assessment covers, how the four phases run, and what the auditor will ask for.

How We Assess Your Cloud Controls

See exactly what we check across all 5 Trust Service Criteria.

What the SOC 2 Process Looks Like

From gap assessment to audit-ready: the full timeline.

How SOC 2 Pays for Itself

One enterprise deal closed covers the engagement many times over.

1 min 29 s · Captions included · Click a chapter to jump to it, or the video to watch it with sound
Book a 15-minute call
The process

The Type I Package, Step by Step

Days 1–3

Gap Assessment

We map your current state against all 5 Trust Service Criteria and agree on the plan.

Days 4–7

Policy Writing

Our policy library adapted to your company, one revision round included.

Days 8–10

Control Implementation

We harden the fix list agreed at the readout, up to 12 Security controls or 20 hours, and set up evidence collection in your platform.

Day 10+

Audit Coordination

We introduce you to our auditor network and take the auditor's questions for 30 days after handoff.

PROOF. NOT PROMISES.

Real Results from Real Clients

Bankingly

SOC 2 Type II for a Platform That Banks Audit

Bankingly powers digital banking for financial institutions across Latin America

"Our clients are banks, so our SOC 2 report gets read line by line. Cloudacio has kept our Type II clean year after year, and audits became routine instead of a fire drill."
Pedro Crosta
VP of Delivery, Bankingly
View Case Study
COSA

From Gap Assessment to a Clean Type II Report

COSA keeps its compliance program audit-ready year round with Cloudacio

"Cloudacio took us from our first gap assessment to a clean Type II report and stayed on to keep us audit-ready. Compliance went from a yearly scramble to something that just runs."
Louise Salinas
Senior VP of Operations, COSA
View Case Study
TrueClaim

SOC 2 Type II for AI-Powered Insurance Claims

TrueClaim's appraisal platform handles carrier data that demands it

"We handle carrier data, so SOC 2 was never optional for us. Cloudacio ran the whole process and our Type II came back clean, without pulling my engineers off product."
Elie Lloyd
Founder, TrueClaim
View Case Study
why us

Why SaaS Companies Trust Cloudacio

Implementation, Not Just Tracking

We fix controls.
Not just find them.

Every compliance platform tells you what's wrong. Cloudacio fixes it: IAM, encryption, logging, VPC, access reviews, vendor management. Your dashboard goes from red to green. Then the auditor comes in.

Auditor Network Access

We introduce
you to auditors.

We don't just prep you and wish you luck. We introduce you to vetted auditors from our network, so you go into the audit with a relationship, not a cold call.

Timeline-Driven Approach

Deal-blocking
timelines met

When a deal depends on your SOC 2 report, we compress the timeline without cutting corners. We've run deal-driven engagements in as little as 45 days to a Type I report. Tell us the deadline. We'll tell you if we can hit it.

45 days
YOUR DELIVERABLES

What You Walk Away With

SOC 2 Gap Assessment

Mapping against all 5 Trust Service Criteria and a prioritized remediation plan, before any billable work begins.

Full Policy Suite

Every required policy: information security, change management, incident response, vendor management, and more. Written for your company.

Control Implementation Support

We work with your engineers to implement missing technical and operational controls. Hands-on, not just advisory.

Audit Evidence Repository

A clean, organized repository of every piece of evidence the auditor needs, mapped to controls and ready to share.

Auditor Introduction

We connect you with a qualified SOC 2 auditor from our network, prep your team, and attend the kickoff.

Post-Audit Support

30 days of support after the audit: the auditor's questions answered and your fixes guided.

ALTERNATIVES

Why Cloudacio vs. the Alternatives

OptionTheir promiseThe reality
Figure it out yourselfFreeYour engineers spend 3–6 months on controls instead of shipping product.
Vanta / Drata alone$15K–$30K/yr SaaSFinds the problems. Nobody fixes them. Most teams stall for 6+ months.
Hire a security engineer$150K–$180K/yr3 months to hire, 3 more to ramp. A single point of failure.
Traditional consultancy$250–$350/hr, open SOWMulti-month engagements and $50K+ bills. Built for enterprise.
CloudacioFree gap, $5K Type IControls hardened, policies written, audit coordinated. Zero failed audits to date.
WHAT YOU GET

An engagement that pays for itself

Your first enterprise customer is typically worth $50K to $200K+. One deal closed covers the $5,000 Type I package ten times over. We scope your free gap assessment on the first call, and no billable work starts until you approve the plan.
ZEROFAILEDAUDITS★ ★ ★MONEY-BACKGUARANTEE★ ★ ★AWS Partner: Select Tier Services
AWS Select Partner
10+ Years in the Cloud
5-Star Client Reviews

Gap Assessment

Free

We map your controls against all 5 Trust Service Criteria and hand you a prioritized remediation plan, before any billable work.

What's included
  • Full mapping of all 5 Trust Service Criteria
  • Prioritized plan with owners and effort
  • Current-state security documentation
  • 30-minute readout call

No billable work until you approve the plan. The remediation plan is yours to keep, whether you fix it with us or without us.

Book the free assessment

SOC 2 Type I

Money-back guaranteeFixed scope
$5,000
Fixed price

Run by senior, certified cloud architects. Typical timeline: 2 weeks once we have access and your kickoff checklist is complete. Covers up to 50 employees, one production account, one product; bigger scope is quoted on the call.

What's included
  • Gap assessment and remediation plan
    Full mapping against all 5 Trust Service Criteria, with owners and timelines.
  • Complete policy suite
    15+ policies from our library, adapted to your company; one revision round included.
  • Control implementation support
    Hands-on hardening of the fix list agreed at the readout, up to 12 Security controls or 20 hours, working with your engineers.
  • Audit evidence repository
    Every piece of evidence organized, mapped to controls, and ready to share.
  • Auditor introduction and coordination
    A vetted auditor from our network, team prep, and support for 30 days after handoff.
Book a 15-minute call

Money-back guarantee: you complete a short checklist on your side, we deliver, or you don't pay.

SOC 2 Type II

Let's scope it

The same team stays with you through the observation window, typically 3 to 6 months. Most teams run $2,500/month compliance sprints until the report lands.

What's included
  • Everything in Type I
  • Control monitoring through the window
  • Continuous evidence collection
  • Full support through the final report

Scoped on your intro call.

Ask about Type II

Testimonials

What Our Clients Say (and Achieve)

What founders and CTOs say about working with Cloudacio.

FAQs

Straight Answers, No Fluff

Here’s everything you need to know before booking your
call.

Who is this for?

SaaS companies facing a SOC 2 requirement: an enterprise prospect's security questionnaire, an investor's diligence checklist, or a compliance platform full of failing controls nobody has time to fix. If a deal or a raise depends on that report, this engagement gets you there.

What do you actually do?

Everything between "we need SOC 2" and the report: gap assessment, policy writing, cloud control implementation, evidence collection, auditor introduction, and audit coordination. Your team approves decisions and provides access, about 2 to 4 hours per week, mostly in the first two weeks. Your engineers keep shipping product.

Do I need to give you full access?

The gap assessment runs on read-only access. For implementation we work through your existing change process: pull requests, infrastructure as code, and scoped roles your team approves. You see every change before it lands, and access ends with the engagement.

We already have Vanta, Drata, or Sprinto. Do we still need you?

Yes, and they work great together. Your compliance platform tracks which controls are failing. We implement the actual fixes to make them pass. Many of our clients come to us specifically because they've had a platform for 6+ months and still haven't gotten across the line.

What's the ROI? How does a $5K engagement make financial sense?

The math is straightforward: the Type I package costs $5,000 and your first enterprise customer is typically worth $50K to $200K+. One deal closed more than pays for everything. Compare that to a security engineer at $150K+ a year and 3 months to ramp, or a consultancy at $250+ an hour on an open-ended SOW.

How long does it actually take?

Type I: typically 2 weeks to audit-ready once we have access and your kickoff checklist is complete; with the auditor's work on top, deal-driven engagements have landed a signed Type I report in as little as 45 days. Type II adds an observation window, typically 3 to 6 months, which most teams work through monthly compliance sprints. The gap assessment comes first and is free: after one call you'll know exactly where you stand.

What if we fail the audit?

We've had zero failed audits for clients where we managed the full readiness process. 30 days of post-audit support is included in every engagement: we answer the auditor's questions and guide your fixes. Remediation beyond the engagement's fix list is quoted separately.

How do we stay compliant after the audit?

Passing the audit is step one. Staying compliant is step two. Most clients keep the same team on monthly compliance sprints through Type II and beyond, and our AI Cloud Ops retainer includes continuous security posture monitoring, IAM misconfiguration scanning, and compliance drift alerts, so problems surface long before your next audit.

Still have questions?

Book a 15-minute call
LET'S TALK ABOUT YOUR SOC 2

15 Minutes to Know Where You Stand

We’ll meet for 15 minutes to understand your stack, your deadline, and what your prospect or investor requires. You’ll leave with a clear picture of what audit-ready takes. No pressure, no hard sell.
JP Olivera
JP Olivera
Founder & CEO·LinkedIn
Prefer to write instead?